Wireless Penetration Testing: WPA3, Enterprise Wi-Fi and the Evil Twin That Still Works
A wireless penetration test shows what someone in your car park can do with your Wi-Fi, without ever plugging into your network. Passphrase cracking, evil twin attacks on enterprise Wi-Fi, guest isolation, rogue access points, and the fixes that work.
Offensive Security
Your wireless network does not stop at the office wall. Anyone in the car park, the lobby or the floor above can receive it, and none of them need a network cable to start an attack. A wireless penetration test checks what such a person can actually do: crack the passphrase, harvest domain credentials through a fake access point, or step from the guest network into systems that should be out of reach.
In short. A wireless penetration test checks four things: whether a pre-shared passphrase can be cracked offline, whether enterprise Wi-Fi leaks domain credentials to a fake access point, whether guest and IoT networks are really isolated, and whether unauthorised access points exist. The most damaging finding is usually the second one: devices that do not check the authentication server's certificate will hand their credentials to an evil twin. The fix is certificate-based authentication with server validation enforced on every device.
What a wireless penetration test covers
A wireless test looks at the radio side of your network the way an attacker in range would. It sits alongside an internal network penetration test, which starts from a device already on the network: the wireless test asks how that device got there.
| Area | What is tested | Typical finding |
|---|---|---|
| Discovery | Every network name, access point, channel, security mode and client in range, including hidden networks | Networks nobody on the IT team knew were broadcasting |
| Pre-shared key networks | Handshake and PMKID capture, then offline cracking of the passphrase | A short or guessable passphrase shared by every device and never changed |
| Enterprise (802.1X) networks | EAP method, server certificate validation on clients, behaviour against a fake access point | Laptops or phones that send domain credentials to any server |
| Guest and IoT networks | Client isolation, routes to internal ranges, reachable management interfaces | Guest Wi-Fi that can reach internal servers or the wireless controller |
| Rogue and evil twin access points | Unauthorised access points on the network, and how clients react to a look-alike | A consumer router plugged into a meeting-room port |
| Signal footprint | Where the signal can be received from outside the building | Corporate Wi-Fi usable from the street or a neighbouring tenant |
Bluetooth, BLE and access-card technologies such as RFID and NFC have their own attack surface and can be included in the same engagement. This article concentrates on Wi-Fi, where most of the findings are.
What a tester uses, and what it shows
Wireless testing needs dedicated hardware: adapters that support monitor mode and packet injection, and directional antennas to measure how far the signal reaches. The software is mostly open source and well known. That is the point: an attacker in your car park has the same tools.
| Tool | What it is used for |
|---|---|
| Kismet, airodump-ng | Passive discovery of networks, access points and clients, including hidden networks |
| hcxdumptool | Capturing PMKIDs and handshakes from pre-shared key networks |
| hashcat | Offline cracking of captured material; mode 22000 covers both PMKID and handshake captures |
| hostapd-wpe, EAPHammer | Running an evil twin against 802.1X networks and capturing the inner authentication |
| bettercap | Network attacks once connected, such as ARP spoofing on a guest network |
| Directional antennas | Measuring signal reach from the car park, the street and neighbouring floors |
WPA2-Personal: the passphrase is the whole defence
On a WPA2-Personal network every device uses the same pre-shared passphrase. An attacker in range can capture the four-way handshake when a device connects, or force one by briefly disconnecting a client. Since August 2018, there has been an easier route: the PMKID attack, published by Jens Steube of the hashcat project, retrieves a crackable value from a single frame that many access points send, with no connected client needed.
Either way the attacker ends up with material they can attack offline, at whatever speed their hardware allows, with no lockout and no log entry on your side. Whether that succeeds depends entirely on the passphrase. A long random passphrase holds; a company name followed by a year does not.
The passphrase is also hard to keep secret. It is on every device, it is often written on the meeting-room whiteboard, and leavers take it with them. If it has not changed in years, assume people outside the company know it.
How strong is strong enough? The Wi-Fi Alliance's guidance is a "non-dictionary, high entropy" passphrase of between 8 and 63 characters. In practice that means a long random string or several randomly chosen words, not a phrase someone thought of, because cracking tools try dictionary words, names, dates and common substitutions first. Some enterprise wireless platforms can also issue a separate pre-shared key per device or group, so one lost device does not mean changing the key for everyone.
- Use a long, random passphrase for any network that must stay on a pre-shared key, and change it when people leave.
- Keep corporate devices off pre-shared key networks altogether. Use 802.1X with certificates for anything that reaches internal systems.
- Where a shared key is unavoidable, for example for some IoT devices, put that network on its own segment with access only to what those devices need.
WPA3-Personal: stronger, with a transition-mode catch
WPA3-Personal replaces the pre-shared key exchange with Simultaneous Authentication of Equals (SAE). The Wi-Fi Alliance, which introduced WPA3 in June 2018, explains the gain: an attacker who records a WPA3-Personal connection cannot take it away and try every password offline, because "the adversary gets only one guess at the password per attack." WPA3 also makes Protected Management Frames mandatory, which stops the forged disconnect messages attackers use to force reconnections.
The catch is transition mode, which lets WPA2 and WPA3 devices share one network name and passphrase while older devices are replaced. In April 2019, researchers Mathy Vanhoef and Eyal Ronen published Dragonblood, a set of attacks that included downgrading WPA3-capable devices in transition mode and side-channel leaks in early SAE implementations. The Wi-Fi Alliance's own deployment guide states the underlying risk directly: "the common password of a WPA3-Personal Transition Mode network can be determined by attacking a WPA2-Personal device using a simple offline dictionary attack." In other words, a transition-mode network is only as strong as WPA2 with the same passphrase.
- Run WPA3-only on networks where every device supports it, and put the remaining WPA2 devices on a separate network with a different passphrase.
- Keep access point and client firmware current, because the early SAE implementation flaws were fixed in updates.
- Use the protections WPA3 added for this. Transition Disable lets a network tell devices that support WPA3 to stop falling back to WPA2, and in the 6 GHz band WPA3 is mandatory: WPA2-Personal cannot be configured there at all.
WPA3 modes at a glance
WPA3 is a family of modes rather than one setting, and choosing the right one for each network matters more than switching on "WPA3" in general.
| Mode | What it does | Use it for |
|---|---|---|
| WPA3-Personal only | SAE instead of the pre-shared key exchange; Protected Management Frames required | Staff and office networks where every device supports WPA3 |
| WPA3-Personal transition mode | WPA2 and WPA3 devices share one network name and passphrase | Migration only, for as short a time as possible |
| WPA3-Enterprise | 802.1X authentication with Protected Management Frames | Corporate devices, ideally with EAP-TLS |
| WPA3-Enterprise 192-bit | EAP-TLS only, 256-bit GCMP encryption, no transition mode | Environments with strict cryptographic requirements |
| Wi-Fi Enhanced Open | Encrypts traffic on open networks without a password, but does not authenticate the network | Guest and public networks that are fully open today |
| SAE-PK | Lets devices verify a public WPA3-Personal network, protecting against look-alike access points | Shared-password networks in lobbies and waiting areas |
The Wi-Fi Alliance's deployment guidance expects WPA3-Personal networks deployed after 31 December 2027 to default to WPA3-only mode, so plan for transition mode to be temporary.
Enterprise Wi-Fi: where domain credentials leak
WPA2-Enterprise and WPA3-Enterprise use 802.1X: each user or device authenticates individually to a RADIUS server, usually against Active Directory. That removes the shared passphrase, but it introduces the most damaging wireless finding we see.
Many networks use PEAP with MSCHAPv2, where the user's domain username and password are checked inside a TLS tunnel to the RADIUS server. The tunnel only protects anything if the device checks that it is talking to your RADIUS server. If it does not, an attacker can broadcast the same network name, present any certificate, and the device will complete the exchange with them. MSCHAPv2 is cryptographically weak: researchers showed at DEF CON in 2012 that a captured exchange reduces to cracking a single DES key. Microsoft's 2013 security advisory on PEAP-MSCHAPv2 described exactly this scenario, warning that a system posing as a known Wi-Fi access point could exploit those weaknesses "to obtain the victim's domain credentials", and advised organisations to "require a certificate verifying a wireless access point before starting an authentication process."
What the evil twin test shows
- The tester broadcasts your corporate network name from a stronger signal than your own access points, for example near a window or entrance.
- Devices configured to connect automatically try to join it and start 802.1X authentication.
- Any device that does not validate the server certificate completes the inner exchange and hands over a challenge and response derived from the user's password.
- The tester cracks that offline. If it succeeds, the result is a working domain credential, obtained from the car park.
Server validation fails in predictable ways: it was never configured, the setting lets users accept an unknown certificate with one tap, the list of trusted servers is missing, or personal devices joined with whatever settings the user chose. A single misconfigured device is enough.
- Move to EAP-TLS, where devices authenticate with certificates instead of passwords. There is no password exchange to capture. Microsoft recommends "moving away from MSCHAPv2-based connections (for example, PEAP-MSCHAPv2 and EAP-MSCHAPv2), to certificate-based authentication (for example, PEAP-TLS or EAP-TLS)". Credential Guard, on by default from Windows 11 22H2 on eligible domain-joined devices, also blocks single sign-on to MSCHAPv2-based Wi-Fi, so many organisations meet this problem during an upgrade.
- Until then, enforce server validation centrally through Group Policy or device management: validate the certificate, trust only the issuing certificate authority, name the specific RADIUS servers, and do not let users approve new servers.
- Keep personal devices off the corporate network, or onboard them through a process that sets these values for them.
Getting server validation right on each platform
- Windows. Push the wireless profile through Group Policy or device management with "Verify the server's identity by validating the certificate" enabled, your RADIUS server names listed under "Connect to these servers", only your issuing certificate authority trusted, and users unable to approve new servers. Microsoft warns that without server authentication, users "might unknowingly connect to a rogue network."
- Android. Since Android 11 QPR1, Android no longer offers "Do not validate" for the CA certificate in enterprise Wi-Fi settings and requires a domain to be set with it. Deploy the profile through device management so the CA and domain match your RADIUS server certificate.
- Apple devices. Use a configuration profile that names the trusted certificate and the trusted server certificate names, so devices accept only your RADIUS servers instead of asking the user.
- Personal devices. Onboard them through a process that installs these settings, or keep them on a separate network with no route to internal systems.
Because the credential is a domain account, this finding connects directly to Active Directory security: what one stolen password reaches inside the network is the subject of the internal test, and an Active Directory security assessment shows how far it goes.
Evil twins, open networks and captive portals
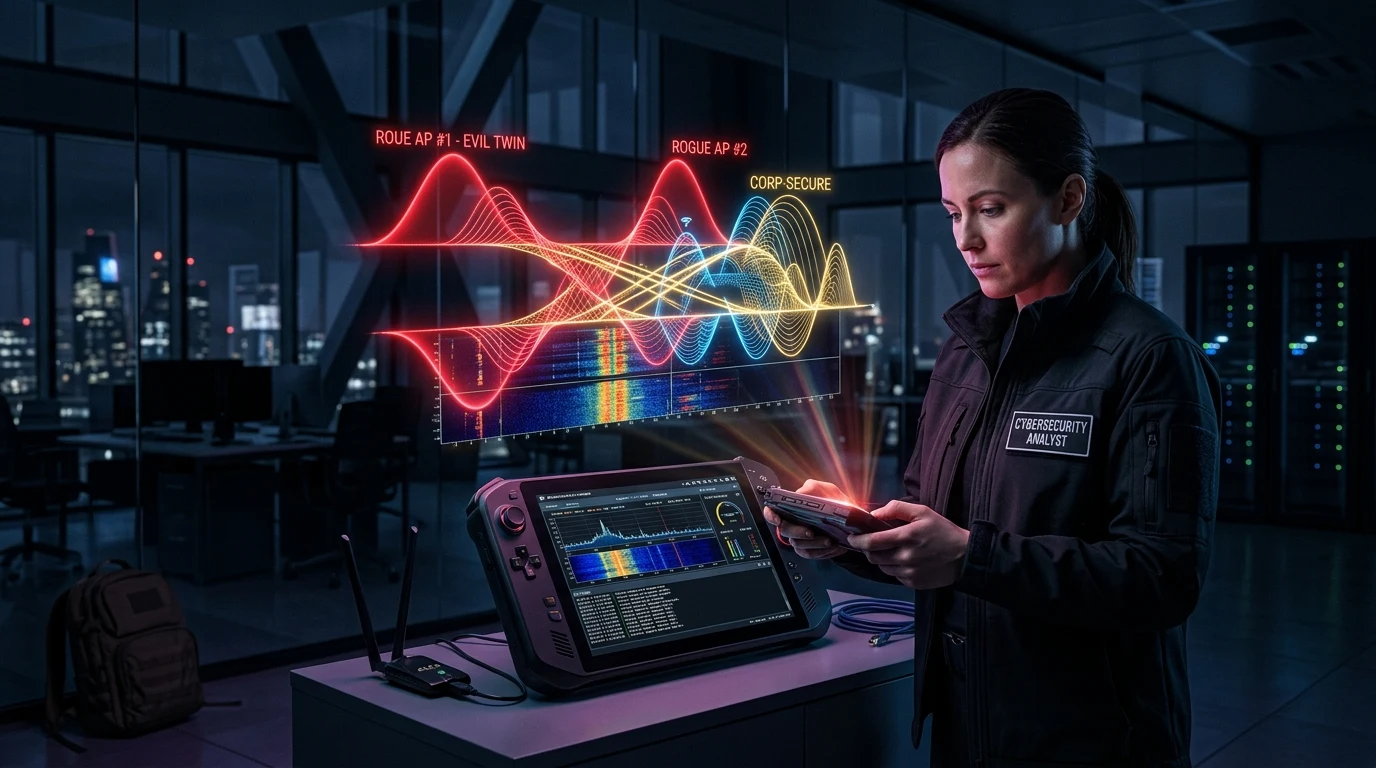
An evil twin is an access point that imitates a legitimate one. MITRE ATT&CK gave it its own technique, T1557.004 (Adversary-in-the-Middle: Evil Twin), in October 2024. Beyond enterprise credentials, a look-alike access point can imitate the guest network or a public hotspot that devices remember, then present a captive portal asking users to "sign in again" with their email password. Testing shows whether devices join automatically, whether users enter credentials, and whether anything on your side notices a second access point broadcasting your network name.
Guest and IoT networks: is the isolation real?
Guest networks are meant to give visitors the internet and nothing else. In testing, they often give a little more: a route to an internal address range, DNS or DHCP served by an internal server, the wireless controller's admin page, or other guests' devices because client isolation is off. IoT networks for cameras, printers and building systems have the same problems and usually weaker devices on them.
The test is simple to describe: join the guest or IoT network as an ordinary user and try to reach anything that is not the internet. Every success is a segmentation gap, and a network architecture review is the place to fix it properly, together with a firewall review of the rules between segments.
From the guest or IoT network, a tester typically tries to:
- Sweep the private address ranges (10.0.0.0/8, 172.16.0.0/12 and 192.168.0.0/16), and IPv6, which isolation rules often forget.
- Check whether DNS resolves internal names and whether DHCP hands out internal servers.
- Reach the wireless controller, access point or switch management interfaces.
- Reach other clients on the same network, which client isolation should block.
- Get past the captive portal, for example by copying the hardware address of a device that has already signed in.
Rogue access points
A rogue access point is one connected to your network without approval: a cheap router plugged in for better meeting-room coverage, or a device left deliberately by an intruder. It bypasses every control on your managed wireless network. If you handle card data, PCI DSS requirement 11.2.1 requires that "the presence of wireless (Wi-Fi) access points is tested for" and that authorised and unauthorised access points are detected and identified at least once every three months. A wireless test checks for them over the air and confirms whether any is actually connected to the wired network, which is what makes it dangerous.
Detecting them. Most enterprise wireless platforms include wireless intrusion detection that can flag an unknown access point broadcasting one of your network names, or a new device bridging onto the wired network. Those alerts only help if someone sees them, so send them to the same place as your other security alerts. On the wired side, 802.1X or network access control on switch ports stops an unapproved device getting network access at all.
Legacy settings still worth checking
- Wi-Fi Protected Setup (WPS). A design flaw disclosed in December 2011 means the eight-digit WPS PIN is checked in two halves, cutting the attempts needed from a hundred million to about 11,000, few enough to try them all. Disable it on anything that still offers it.
- WEP and TKIP. Both are broken. They still appear on networks kept alive for old handheld scanners, payment terminals or medical and industrial devices.
- Unpatched clients and access points. The KRACK attacks published in October 2017 targeted the WPA2 handshake itself and needed patches on both clients and access points. Devices that never received those patches remain exposed, which is one more reason to retire legacy equipment or isolate it.
How a wireless penetration test runs
A wireless security test is planned around your sites and networks: larger estates need more time on site, and cracking and reporting continue after the testers leave.
Step 1 — Scope and authorisation
Agree the sites, the network names and access points in scope, and written authorisation. Networks belonging to neighbours or other tenants are never tested, even when they are in range.
Step 2 — Passive discovery
Listen before touching anything: every network, access point, client and security mode in range, inside the building and from outside it.
Step 3 — Active testing
Handshake and PMKID capture and cracking, the evil twin test against enterprise networks, rogue access point checks, and isolation testing from guest and IoT networks.
Step 4 — Follow the access
Where a test produces a credential or network access, show what it reaches, within the agreed limits, so the finding is reported by impact rather than by technique. This is where a wireless test hands over to a network penetration test.
Step 5 — Report and retest
Each finding with its evidence and a specific fix, then a retest to confirm the fix worked on the devices that matter.
What a good wireless test report contains
A wireless finding is only useful if the team that fixes it can reproduce it and confirm the fix. For each finding, expect:
- The affected network name, access point and the location where the issue was reproduced.
- Evidence: the capture, the type of material recovered and how long it took to crack, or the device that joined the evil twin.
- What the access reached, so the finding is rated by impact.
- The exact fix, down to the setting or policy that needs to change.
- A retest result once the fix is in place.
The report should also include a map of where your signal can be received from outside the building. It is often the finding that changes how people think about wireless risk.
Preparing for a wireless penetration test
- A list of the sites, buildings and floors in scope, and the network names you own.
- Written authorisation, including for testing from car parks or shared areas you do not control.
- A test laptop and phone set up the way staff devices are, so enterprise authentication is tested against real configurations.
- Contacts in IT and facilities for the test days, and any times to avoid.
- Confirmation that networks belonging to neighbours and other tenants are out of scope, even though they are in range.
A wireless hardening checklist
| Control | Why it matters |
|---|---|
| EAP-TLS for corporate devices | No password exchange for an evil twin to capture |
| Server validation enforced by policy | One device that trusts any server is enough to leak a credential |
| WPA3-only where devices support it | SAE resists offline cracking; transition mode keeps the WPA2 weakness |
| Long random passphrases, changed on leavers | The passphrase is the only defence on a pre-shared key network |
| Protected Management Frames on | Stops forged disconnects used to force reconnections |
| Guest and IoT networks isolated and tested | Isolation that has not been tested from the inside is an assumption |
| Rogue access point detection | An unapproved access point bypasses every wireless control you have |
| WPS, WEP and TKIP disabled | All three have known, practical attacks |
Frequently Asked Questions
Click any question to expand the answer.
QWhat is a wireless penetration test?
An authorised test of your wireless networks from the position of an attacker in radio range. It covers passphrase cracking on pre-shared key networks, how enterprise Wi-Fi authentication behaves against a fake access point, whether guest and IoT networks are isolated, and whether unauthorised access points exist. Bluetooth, BLE and access-card technologies can be included.
QCan someone attack our Wi-Fi from outside the building?
Yes. Anyone who can receive your signal, in the car park, a neighbouring office or the street, can capture handshakes, broadcast a look-alike network and try to join yours. That is why a wireless test includes measuring where the signal can be received from outside.
QIs WPA2 still secure?
WPA2-Enterprise with certificate-based authentication and enforced server validation remains strong. WPA2-Personal is only as strong as its passphrase, because captured handshakes can be attacked offline; the Wi-Fi Alliance advises a non-dictionary, high-entropy passphrase and recommends WPA3 whenever possible.
QIs WPA3 secure?
WPA3-Personal is a real improvement: SAE stops offline dictionary attacks against recorded connections, and Protected Management Frames are mandatory. The early Dragonblood implementation flaws from 2019 were fixed in updates. The main remaining risk is transition mode, where the same passphrase also works over WPA2.
QWhat is the PMKID attack?
A technique published in August 2018 by Jens Steube of the hashcat project. It obtains a crackable value from a single frame that many WPA and WPA2 access points send, without waiting for a client to connect. The value is then attacked offline, so a strong passphrase is the only defence.
QWhat is an evil twin attack?
A fake access point that copies the name of a legitimate network so devices connect to it. Against enterprise Wi-Fi it can capture credentials from devices that do not validate the server certificate. MITRE ATT&CK lists it as T1557.004.
QWhy is PEAP-MSCHAPv2 risky?
If devices do not validate the RADIUS server certificate, an evil twin can complete the exchange and capture a challenge and response derived from the user's domain password, which can be cracked offline. Microsoft recommends moving to certificate-based authentication such as EAP-TLS.
QHow often should wireless networks be tested?
PCI DSS requirement 11.2.1 requires testing for wireless access points at least every three months where card data is in scope. NIST SP 800-153 recommends periodic technical security assessments of wireless networks at least annually. Test again after significant changes such as new sites, controllers or authentication methods.
QWhat tools are used in a wireless penetration test?
Dedicated wireless adapters and directional antennas, plus widely available software: Kismet or airodump-ng for discovery, hcxdumptool for capturing handshakes and PMKIDs, hashcat for offline cracking, and hostapd-wpe or EAPHammer for evil twin tests against enterprise networks. Attackers use the same tools.
QWhat is Wi-Fi Enhanced Open?
A Wi-Fi Alliance mode based on Opportunistic Wireless Encryption (RFC 8110) that encrypts traffic on open networks without a password. It protects against passive eavesdropping but does not authenticate the network, so it suits guest and public networks rather than corporate access.
QDoes a wireless penetration test need to be done on site?
Yes. Wireless testing needs radio range, so testers work on site, both inside the building and from the places an attacker could stand outside it, using dedicated wireless hardware.
QWill a wireless penetration test disrupt our network?
Most of the work is passive listening. A few tests, such as briefly disconnecting a test client to capture a handshake or running a look-alike access point, can affect users for a moment, so they are agreed in advance and limited to test devices or quiet periods.
Related reading
For what happens after a device is on the network, see what an internal network penetration test finds. For the directory those credentials belong to, Active Directory security: hardening against modern attacks. For when to use a penetration test and when a red team, red team vs penetration testing.
Sources
- Wi-Fi Alliance, Wi-Fi Alliance introduces Wi-Fi CERTIFIED WPA3 security.
- Wi-Fi Alliance, WPA3 and Wi-Fi Enhanced Open Deployment Guide.
- Mathy Vanhoef and Eyal Ronen, Dragonblood: analysing WPA3's Dragonfly handshake.
- hashcat, New attack on WPA/WPA2 using PMKID.
- Microsoft, Security Advisory 2876146: Wireless PEAP-MS-CHAPv2 authentication could allow information disclosure.
- Microsoft, Credential Guard: considerations and known issues.
- Microsoft, Extensible Authentication Protocol (EAP) for network access.
- MITRE ATT&CK, T1557.004 Adversary-in-the-Middle: Evil Twin.
- PCI Security Standards Council, PCI DSS v4.0.1, Requirement 11.2.1.
- NIST, SP 800-153, Guidelines for Securing Wireless Local Area Networks.
- CERT/CC, VU#723755: WPS PIN brute force vulnerability.
- Mathy Vanhoef, Key Reinstallation Attacks (KRACK).
- Android Developers, Secure Wi-Fi Enterprise configuration.
- IETF, RFC 8110: Opportunistic Wireless Encryption.
Adayptus Consulting
Offensive Security, Adayptus
Adayptus Consulting Private Limited is a cybersecurity consultancy based in Noida, India, testing wireless networks on site with dedicated hardware, from inside the building and from outside it.
On This Page
- What a wireless penetration test covers
- What a tester uses, and what it shows
- WPA2-Personal: the passphrase is the whole defence
- WPA3-Personal: stronger, with a transition-mode catch
- WPA3 modes at a glance
- Enterprise Wi-Fi: where domain credentials leak
- Evil twins, open networks and captive portals
- Guest and IoT networks: is the isolation real?
- Rogue access points
- Legacy settings still worth checking
- How a wireless penetration test runs
- What a good wireless test report contains
- Preparing for a wireless penetration test
- A wireless hardening checklist
- Frequently Asked Questions
- Related reading
- Sources