
Four ways we secure your business
Manual, expert-led testing, 24×7 monitoring, cloud assurance and compliance readiness — delivered by senior consultants who verify every finding before it reaches you.
Penetration Testing
Web, API, mobile, network & cloud — manual, not scanned
Learn moreManaged SOC & MDR
24×7 monitoring, threat hunting and incident response
Learn moreCloud Security
AWS, Azure & GCP posture, identity and workload review
Learn moreCompliance & GRC
ISO 27001, SOC 2, RBI, SEBI and DPDP readiness
Learn moreOSCP & CISSP
Certified Consultants
24/7 Expert-led
Threat Monitoring
Zero False Positives
Actionable Insights
NDA-backed
Confidentiality
Dealing with an incident right now?
Our incident response team is on standby 24×7. If personal data may be involved, CERT-In reporting runs to a six-hour clock from detection.
- OSCP & CISSP-certified consultants
- Manual, expert-led testing
- Zero false positives
- Actionable, developer-ready reports
- Free remediation retest
- NDA-backed confidentiality
Strengthening resilience across industries.
24×7 Expert-led threat monitoring.
Offensive Security, Cloud & GRC.
Aligned to business & compliance goals.
Measurable risk reduction & confidence.
Compliance & Industry Framework Alignment
Our Approach
Engineering Digital
Resilience
We go beyond simple compliance. Our team integrates deeply with your engineering and operations to build security into the DNA of your organization.
Proactive Defense
Identifying threats before they impact operations.
Strategic Alignment
Security that enables, rather than hinders, business growth.
Expert Partnership
Direct access to senior security architects and engineers.
Our Core Security Expertise
Delivering end-to-end cybersecurity solutions tailored to your specific infrastructure and business risks.
Start with what is driving it
Working to a deadline?
Most security work starts with an obligation rather than a shopping list — a regulator, an auditor, or a customer questionnaire. We work to frameworks across North America, the EU, Africa and Asia. Find yours below.
Or by your sector
Security shaped around your industry
Regulatory pressure, threat profile and acceptable downtime differ by sector — so the assessment should too.
Latest Security Insights
Stay ahead of threat actors with expert analysis on emerging vulnerabilities, compliance updates, and defensive strategies.
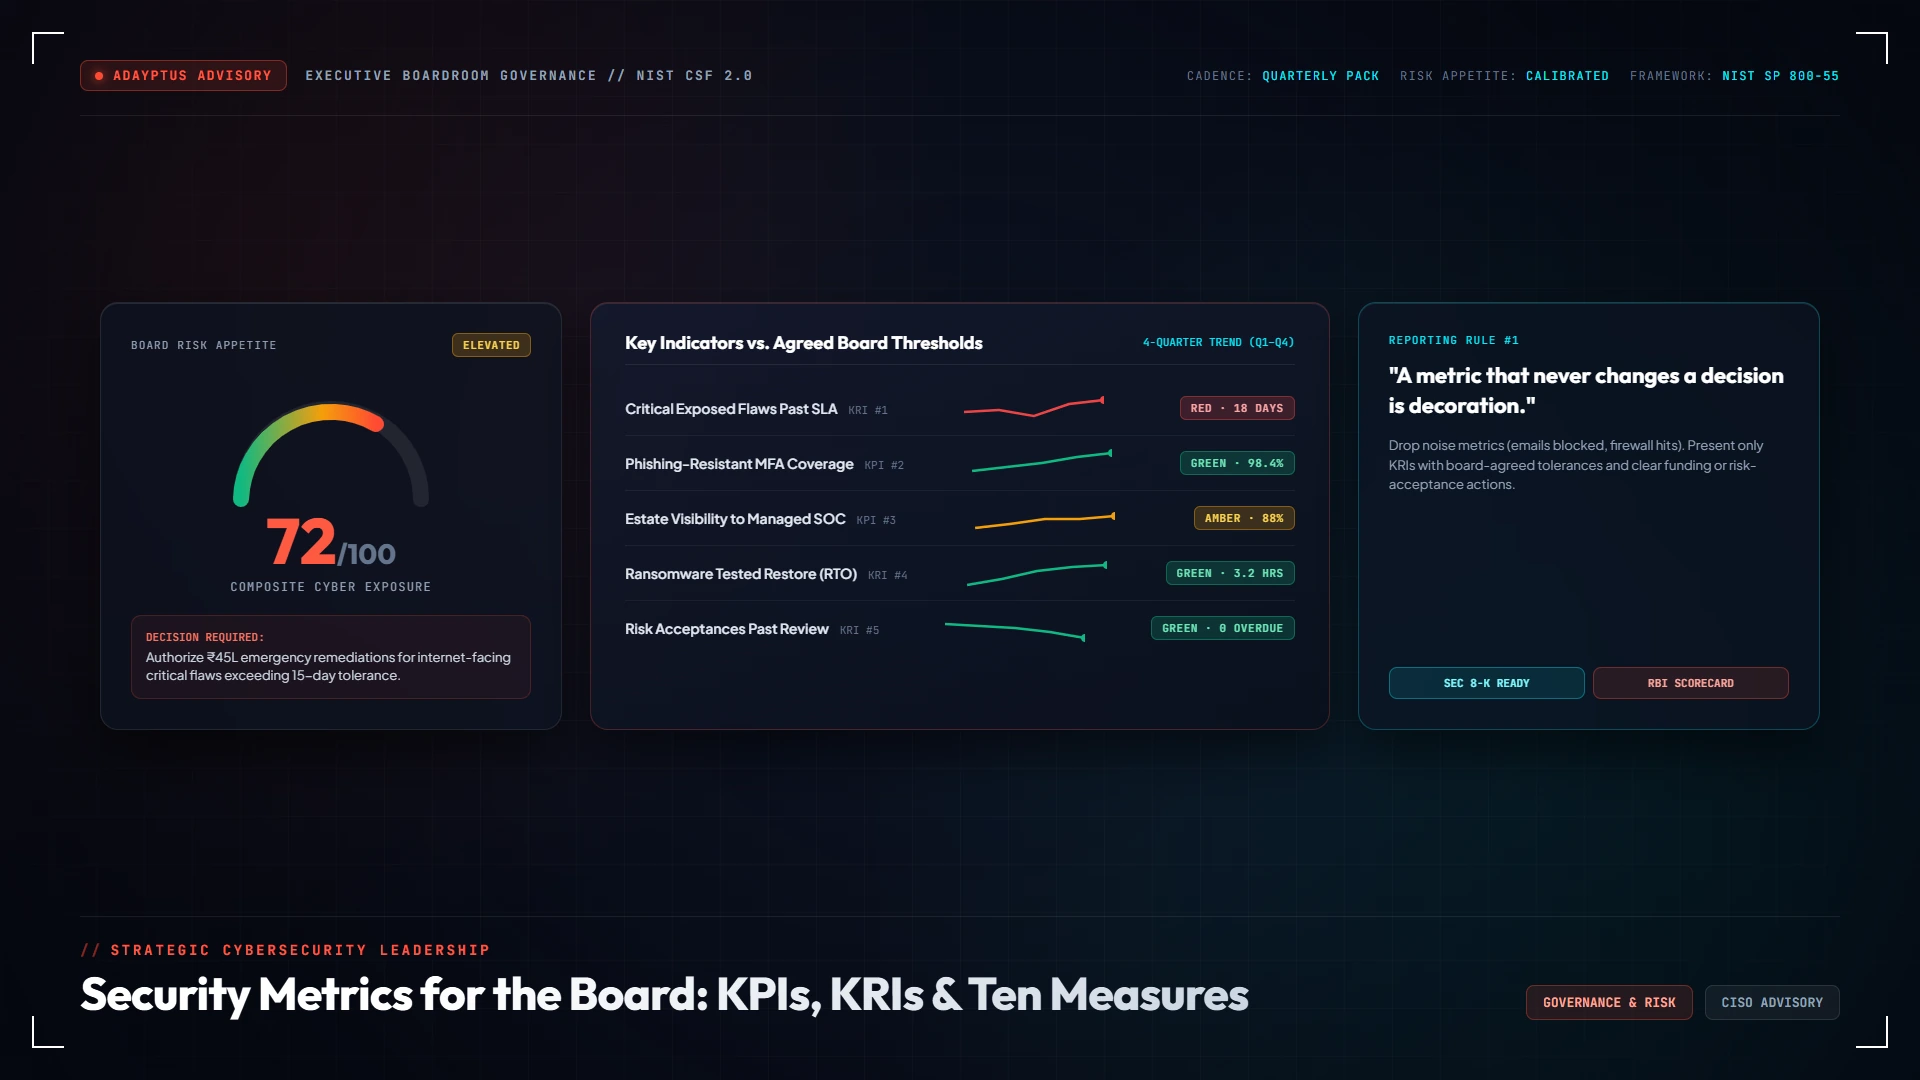
Security Metrics for the Board: KPIs, KRIs and Ten Measures Worth Reporting
Most board security dashboards report activity, not risk. The difference between activity metrics, KPIs and KRIs, ten measures worth reporting, the ones to leave out, and how to present them so they lead to decisions.
Read Article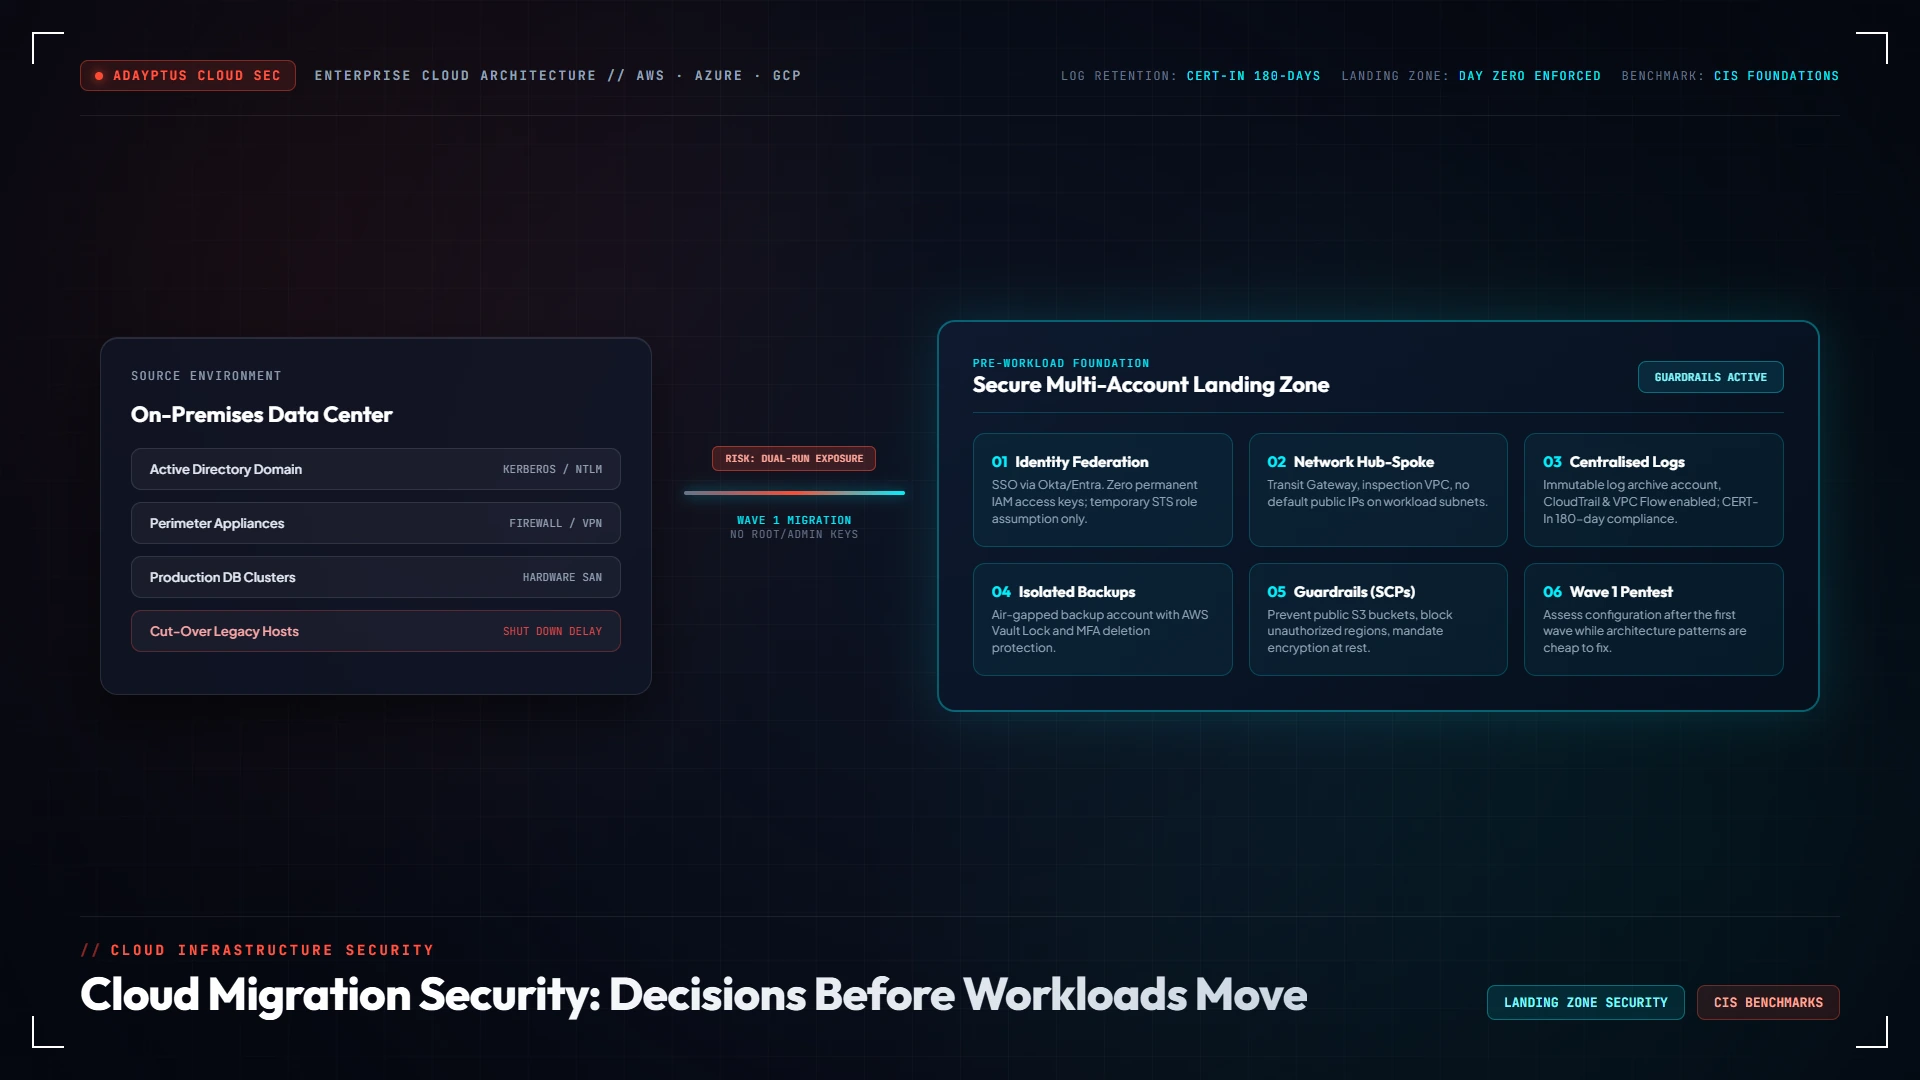
Cloud Migration Security: The Decisions to Make Before the First Workload Moves
Most cloud weaknesses are decided, or left undecided, during the migration. The landing zone, identity, network, logging, data and backup decisions to make first, the risks specific to the migration itself, and when to assess.
Read Article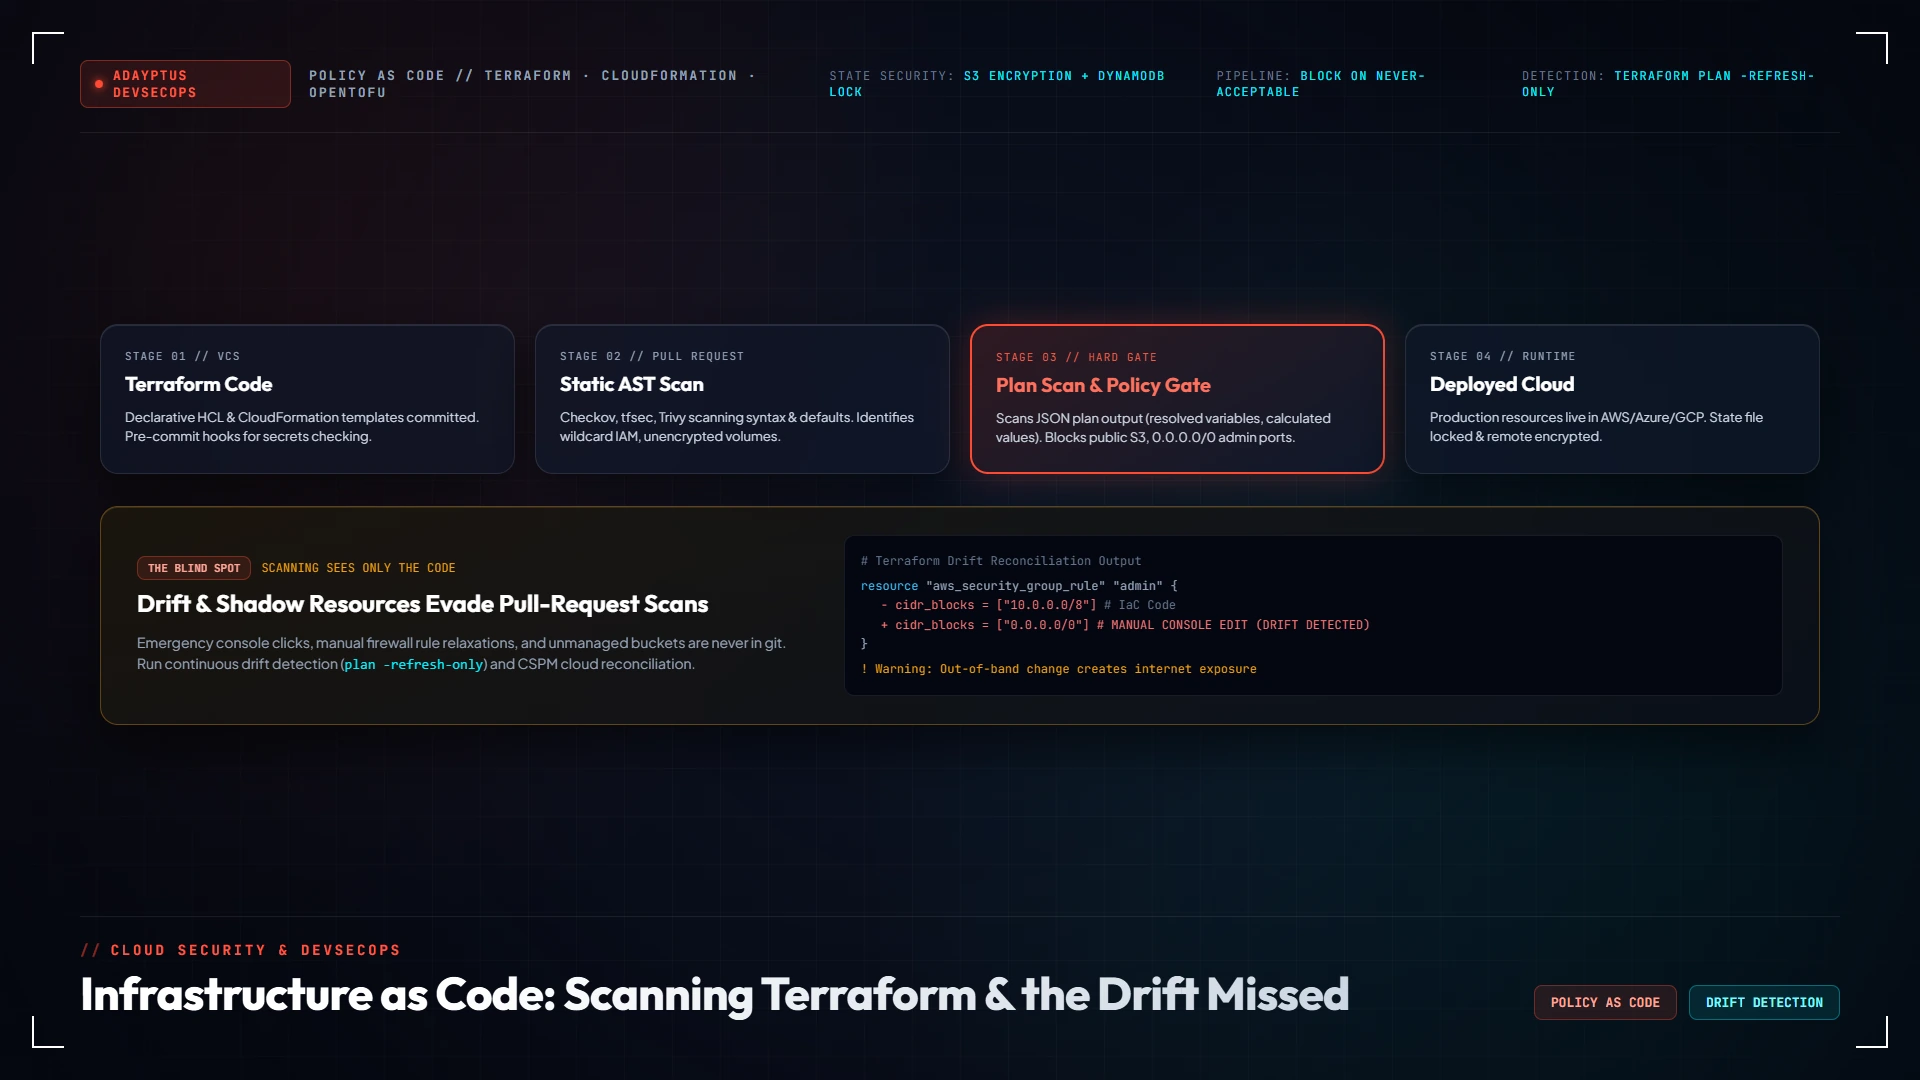
Infrastructure as Code Security: Scanning Terraform and CloudFormation, and the Drift Scanners Miss
Infrastructure as code is the cheapest place to stop a cloud misconfiguration, but scanning only sees what is in the code. Where to scan, what to block, how to protect state and the pipeline, and how to catch drift and unmanaged resources.
Read ArticleReady to Secure Your Digital Infrastructure?
Tell us what you need assessed and a senior consultant will come back with scope, timeline, and an indicative quote — usually within one business day.
- Senior consultants, not junior scanners
- Findings prioritised by real exploitability
- Clear scope and pricing before you commit
- Covered by NDA from the first conversation
Request a scoping call
No obligation. A senior consultant replies — not a sales sequence.